
Pentester
Paid to break into systems within agreed rules, then explain clearly enough that someone actually fixes it.
Role at a glance
The shape of the job
Pay bands are TechWaymark practitioner estimates for UK roles, reviewed 2026-09, not survey data. They vary by region, sector and employer.
What the Pentester role involves
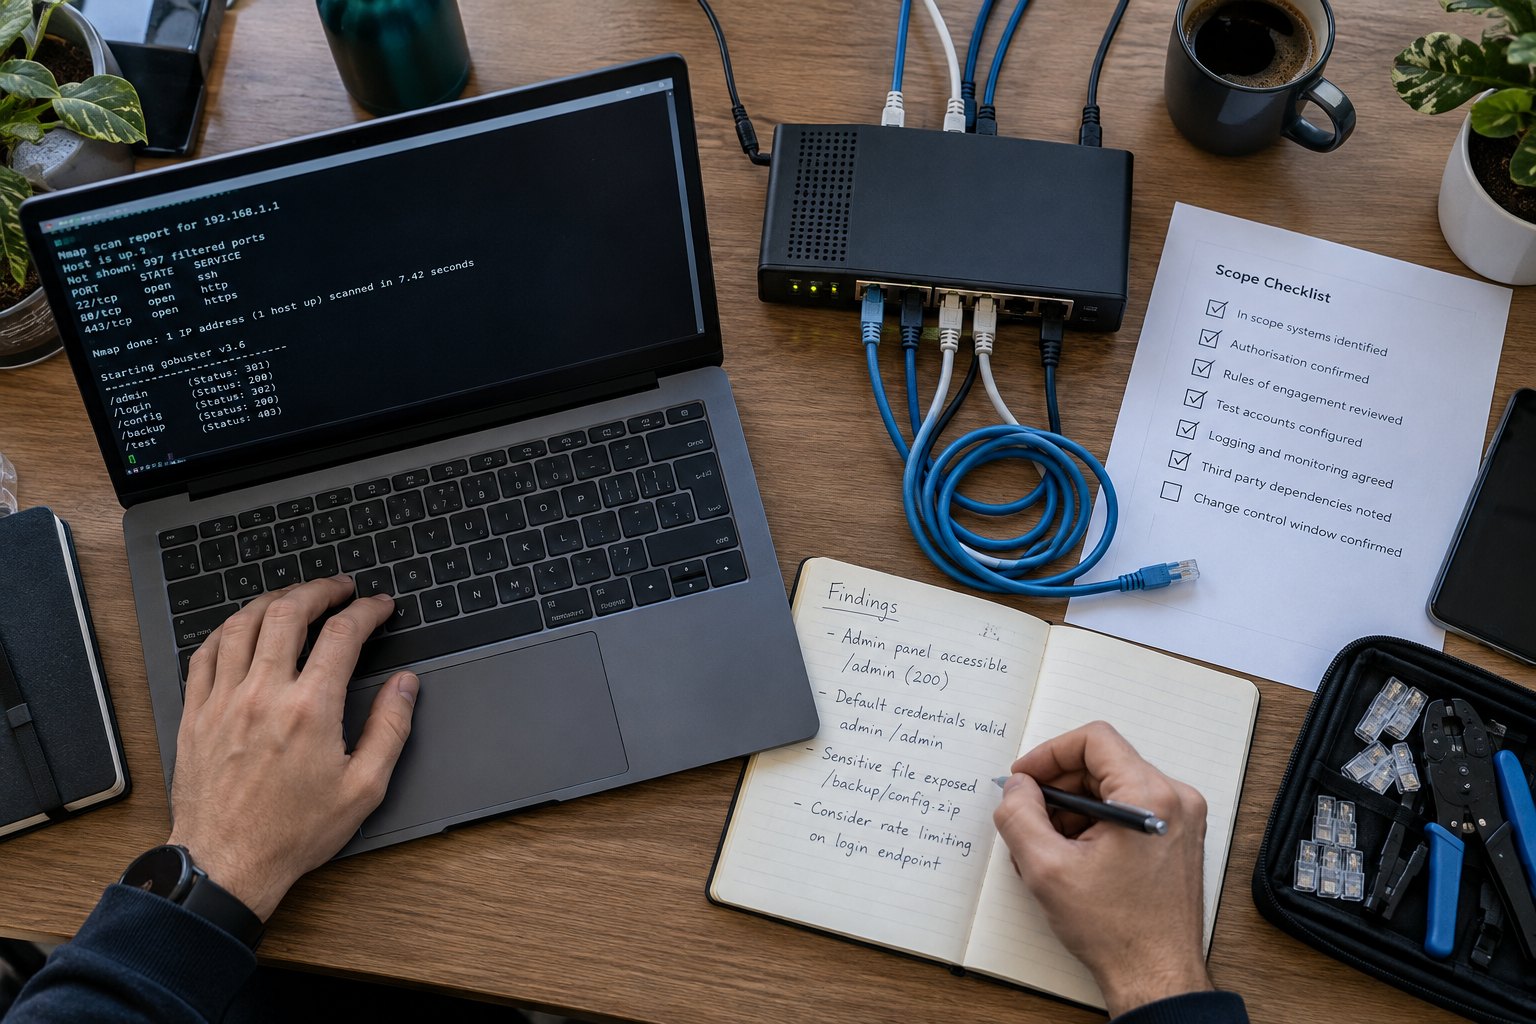
- You test web apps, networks or cloud setups against an agreed scope and time box, usually a few days per job.
- You find weaknesses, prove they matter by showing what an attacker could reach, and stop there.
- You write a report that a developer can fix from and a manager can make a decision from. Those are two different readers.
- You retest after fixes and confirm what's closed and what isn't.
Read TechWaymark's full role verdict and reasoning
An assessment role where permission, reproducibility and useful reporting matter alongside finding vulnerabilities.
- Domain
- Cybersecurity
- Entry
- Not mapped
- Senior
- Not mapped
- You've already got writeups, CTF solves or HTB ranks that prove the hands work
- You'll happily write a 40-page report for every fortnight of testing
- You can sit with not knowing the answer for days at a time
- You enjoy reading other people's code more than writing your own
- You are seeking unsupervised assessment work before practising scope, findings and reporting
- You want offensive work without the consultancy travel or scoping calls
- You don't like being wrong in writing, in front of clients, every quarter
What "doing well" looks like in the seat
- Your reports get used as templates by the rest of the team
- You find things that aren't on the checklist
- Clients ask for you by name on the rebook
- You're shipping tooling or research between engagements, not just consuming both
Engagement scope and reporting deadlines can constrain the investigation. Clarify travel, retest expectations and how findings are reviewed before delivery to clients.
Illustrative
An onsite testing day
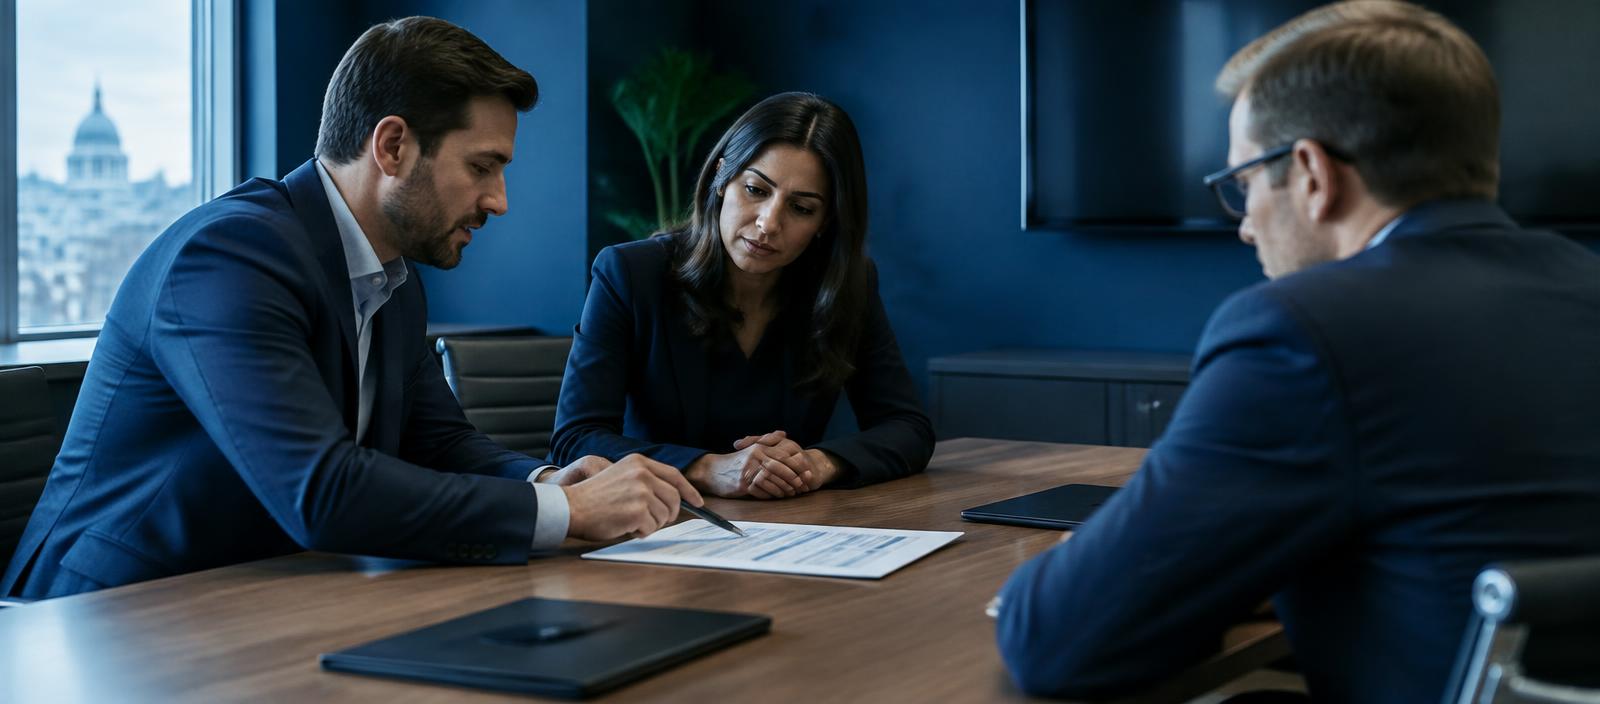
- Meet the client contact onsite. Check access works and whether anything has changed since the scope was agreed
- Begin testing the agreed web application and its user permissions, using the supplied test accounts
- Confirm that one test account can access another account's invoice. Record the evidence and promptly notify the agreed client contact
- Continue testing within the agreed scope, checking how widely the access issue applies
- Complete further checks and organise the day's evidence and findings for the report
- Hold the daily wash-up with the client: explain what was tested, discuss findings and blockers, and agree tomorrow's testing
An example day. Roles and organisations vary, and no two days match.
Day to day
What you'll work with
Systems
Tools
Concepts
Hiring reality
What employers actually expect
Must understand
- Stay inside scope, always
- Explain a finding in plain English
- Understand how systems work before trying to break them
- Keep careful notes
Commonly expected
- Networking and web fundamentals
- Linux comfort
- Some scripting
- A practical cert such as OSCP, PNPT or CPTS
Sets you apart
- Clear public write-ups
- Prior IT, development or SOC experience
- Active Directory attack knowledge
- Reports a non-technical manager can act on
What this role isn't
It isn't hacking whatever you like, and it isn't mostly exciting exploits. Much of it is methodical checking, careful evidence and writing. Without written permission, the same activity is a crime.
How the role changes with seniority
Works alongside seniors on tests, runs checks, drafts findings for review.
Leads tests alone, handles the client, writes and defends the report.
Scopes work, reviews others' reports, handles the hard jobs and trains the team.
Nobody puts this in the advert
The hard parts
A crowded entry point
Many people want this job with only labs behind them. Hiring managers usually want something more.
Report writing
It can be half the job. People who only enjoy the testing often struggle.
Utilisation targets
Consultancies bill by the day. Back-to-back jobs and tight deadlines are normal.
Seeing the same issues
The tenth missing patch report of the month is less exciting than the films suggest.
More than one way in
How people actually get into it
From IT, dev or SOC
The most common path. Knowing how systems are built and run makes you a better tester.
Graduate or junior consultant scheme
Some consultancies train juniors, usually after a practical assessment.
Practical certs plus write-ups
OSCP, PNPT or CPTS with public write-ups can get you to interview. It rarely works on certs alone.
Internal move
Larger firms with in-house testing teams sometimes take people from their own IT or security teams.
Evidence employers value
"Rooted 100 boxes"
Three write-ups showing your method, what didn't work, and how you'd explain the risk to a client
"OSCP certified"
OSCP plus a sample report you wrote from a lab, with a clear risk rating and fix
"Passionate about ethical hacking"
A responsible disclosure you made, and how you handled it
Projects that prove it
Small pieces of work you can do on your own, and what each one shows an employer.
Write a real-style report
3-4 eveningsTest a deliberately vulnerable app such as OWASP Juice Shop. Produce a client-ready report with summary, findings, risk ratings and fixes.
What it demonstrates
Attack a small AD lab
2 weekendsBuild a domain with a couple of common misconfigurations, then find and exploit them. Record how a defender would spot each step.
What it demonstrates
Scope a pretend engagement
1 eveningWrite a one-page scope and rules of engagement for a fictional client: what's in, what's out, stop conditions and contacts.
What it demonstrates
Your next hops
Where Pentester can take you
Other common branches
There is no single ladder. See the routes on the Atlas.
Worth the effort?
Certifications that complement it
The best-known practical exam. Still asked for by name on many UK adverts.
See certification verdict PNPTPractical exam with a report and debrief, closer to real client work than most.
See certification verdict CPTSDemanding hands-on exam with a strong Active Directory and reporting element.
See certification verdict GIAC GPENRespected but expensive. More often funded by an employer than self-funded.
See certification verdictInterview reality
Questions you may be asked
Loading questions…
Practise with model answers in My WaymarkFor educators
Used in TechWaymark Education
These modules use this page as investigation material in the classroom.
- 1Technology is not one career
An example of work that protects systems by testing them, within strict rules
Could you realistically get here from where you are?
The Guided Route compares your background with this role and shows the honest route, hop by hop.
Last reviewed 2026-09. Photographs are illustrative.