The work itself
What you would spend time doing
Test an agreed scope, reproduce weaknesses and explain their impact and remediation. Client communication, evidence handling and retesting are part of the engagement.

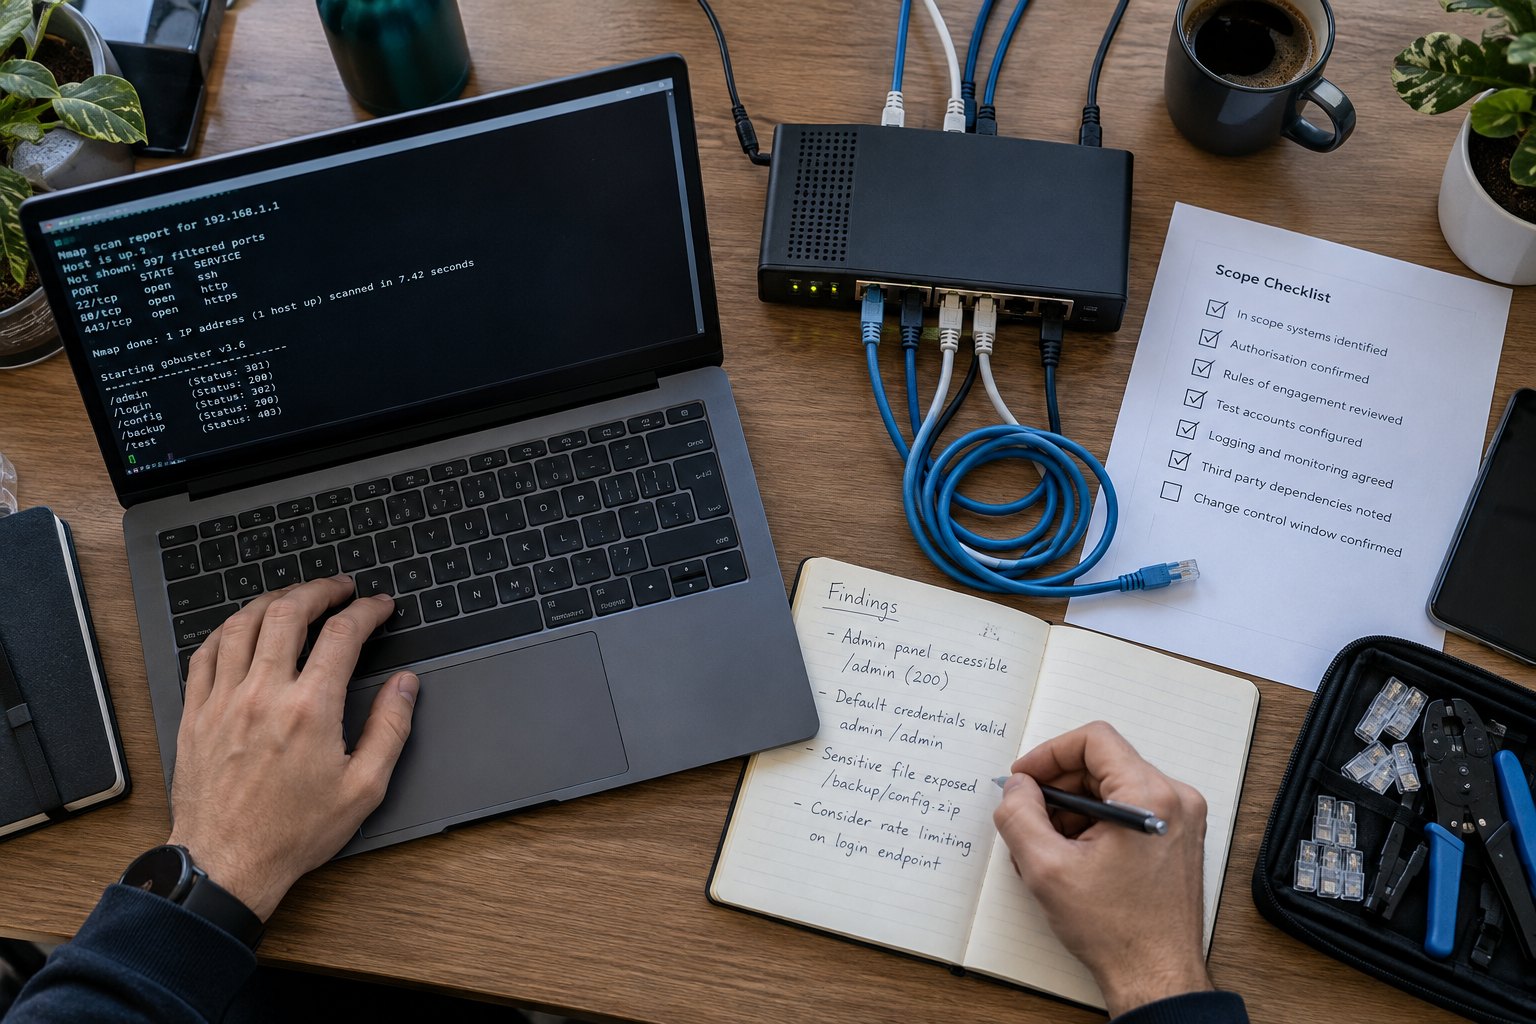
An assessment role where permission, reproducibility and useful reporting matter alongside finding vulnerabilities.
Explore the work, check your starting point and try one scoped task before committing to a course or exam.
Try this pathway in practiceThe route
A general route, not a personal plan. Linked guides describe the broader role family; a junior or support starting point may have a narrower remit. Compare the responsibilities with the actual vacancy.
Build on your existing experience, demonstrate the next responsibility and review it with the people who rely on your work.
Progress through demonstrated capability and agreed responsibility. These stages are not a fixed timetable or a salary ladder.
Build on existing experience
Review your existing work against Junior Pentester or AppSec Engineer responsibilities. Identify one gap in judgement, delivery or ownership and agree a scoped way to demonstrate it.
A short account of what you can already do and the next gap to investigate.
In focus CRTO · Burp Suite Certified Practitioner
Demonstrate readiness
Explore Junior Pentester or AppSec Engineer responsibilities. Check the supervision and prior experience expected; demonstrate the relevant work before increasing your scope.
A concise finding with scope, reproduction steps, impact, remediation and retest result.
In focus Junior Pentester or AppSec Engineer
Demonstrate reliable practice
Take on a scoped responsibility, test your decisions and collect feedback. Add a credential only where it supports that work.
A test record and feedback showing how you improved a piece of work.
In focus eJPT · PNPT
Broaden responsibility
Red Team Lead or Adversary Simulation. The operational shift from operator to designer.
Examples of broader ownership, with the scope and responsibility agreed.
In focus OSEP
The work itself
Test an agreed scope, reproduce weaknesses and explain their impact and remediation. Client communication, evidence handling and retesting are part of the engagement.
Your starting point
Understand web or network fundamentals before specialising. Practise only in explicitly authorised labs; exam success does not establish readiness to run a client engagement alone.
Ask a course provider or employerWho approves scope changes and reviews findings before they reach the client?
You've already got writeups, CTF solves or HTB ranks that prove the hands work. You'll happily write a 40-page report for every fortnight of testing.
Engagement scope and reporting deadlines can constrain the investigation. Clarify travel, retest expectations and how findings are reviewed before delivery to clients.
Study options, not a checklist. Choose for the work you need to demonstrate, then check the provider’s current requirements and renewal terms.
Explore these first
Compare the subject with the work you want to do. Check eligibility before committing.
For a particular platform or gap
Choose one when its syllabus addresses a gap you need to practise.
Detailed guide not yet available. Check the issuer's syllabus and entry requirements.
As your responsibility grows
Revisit when your scope changes. Experience and renewal requirements still apply.
Produce something you can explain, test and improve with feedback.
A scoped starting exercise
Choose one deliberately vulnerable training application you are authorised to test. Define the scope, reproduce one finding and retest an available fix within the lab.
What to keepA concise finding with scope, reproduction steps, impact, remediation and retest result.
Free text worksheet · no account needed. Add your checks, results and feedback as you work.
Label planned, simulated and completed work accurately. A practice exercise helps you test your interest and reasoning; it does not establish production experience or guarantee an interview.
Check these assumptions against the course, vacancy or team you are considering.
That a title or credential establishes readiness by itself. Compare the advertised supervision with your evidence of authorised testing, reproducible findings and clear reporting.
Compare the advertised supervision with your evidence of authorised testing, reproducible findings and clear reporting. Direct junior entry and transitions from other roles are both possible; no duration guarantees either.
What this is based on
Editorial route and career guidance. No separate external evidence review is recorded for this assessment.
Editorial evidence review: pending · UK market. Vendor facts and prices elsewhere on this page have their own sources and check dates.